Reference photos
Customer-authorized images submitted through the authenticated reference workflow.
Trust and privacy
This internal/test page describes controls present in the repository and links each claim to dated engineering evidence.
This is not a certification, audit opinion, uptime promise, DPA, or public security statement. The claim registry and evidence date are September 29, 2026.
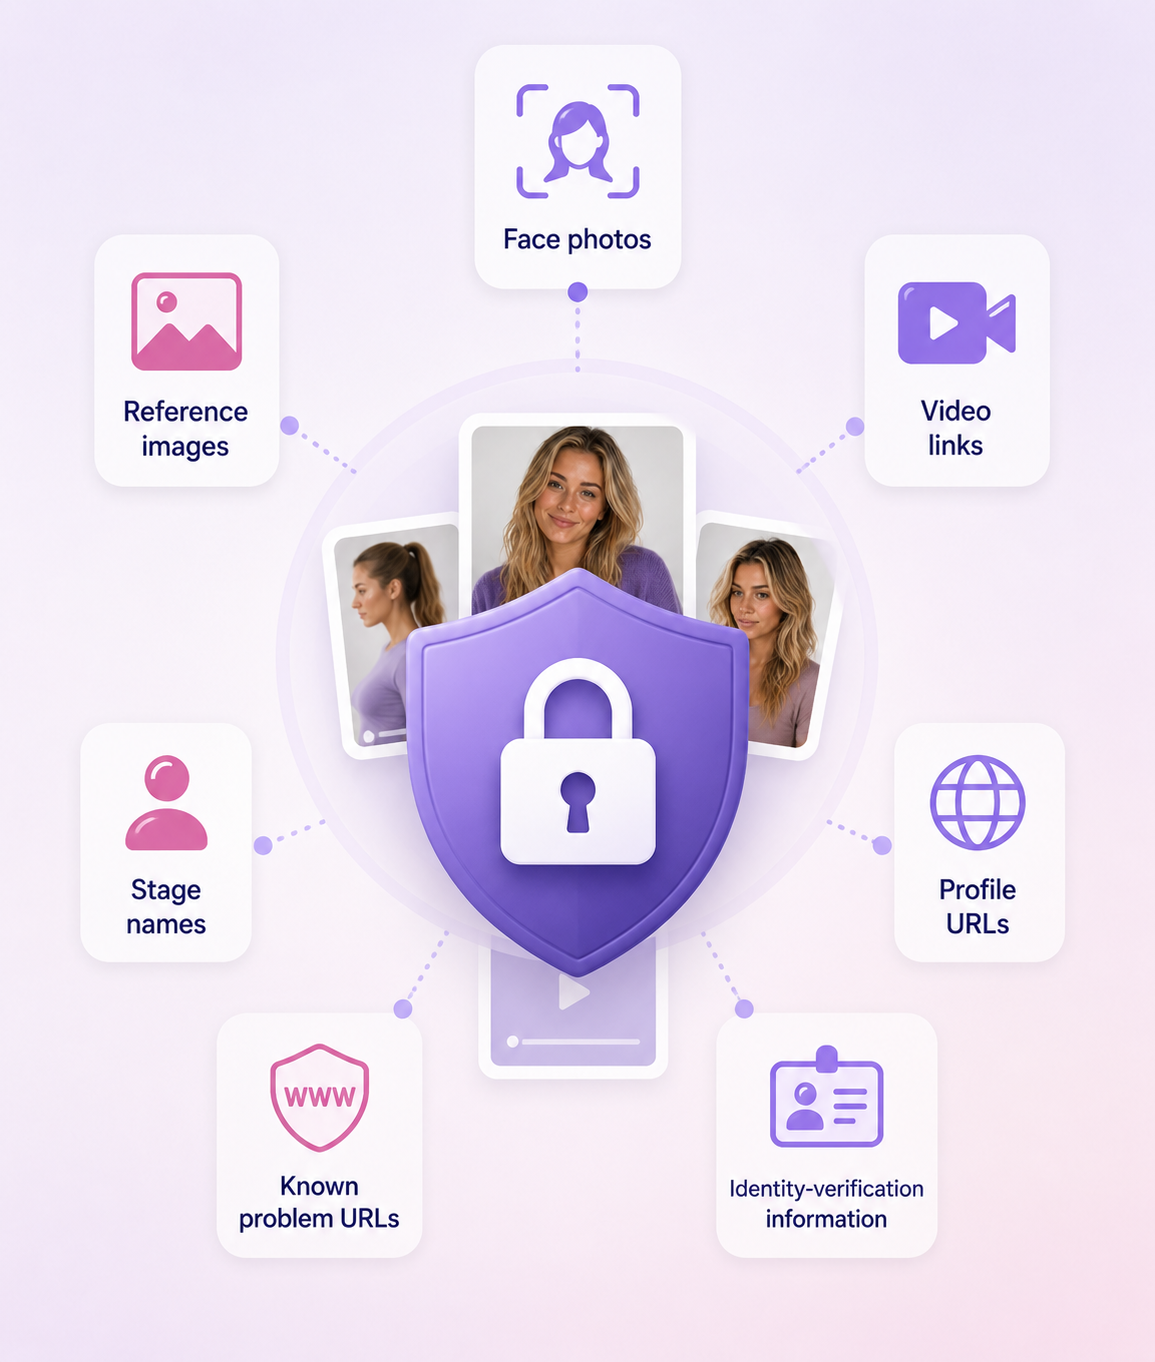
What you upload
Customers may add face photos, optional references, video links, profile URLs, stage names, known problem URLs, and identifying-feature notes.
Customer-authorized images submitted through the authenticated reference workflow.
Stage names, aliases, public links, and known problem URLs.
Context for stolen video or frame-related monitoring workflows.
Authority state is recorded only by supported workflows; this page does not claim independent identity verification.
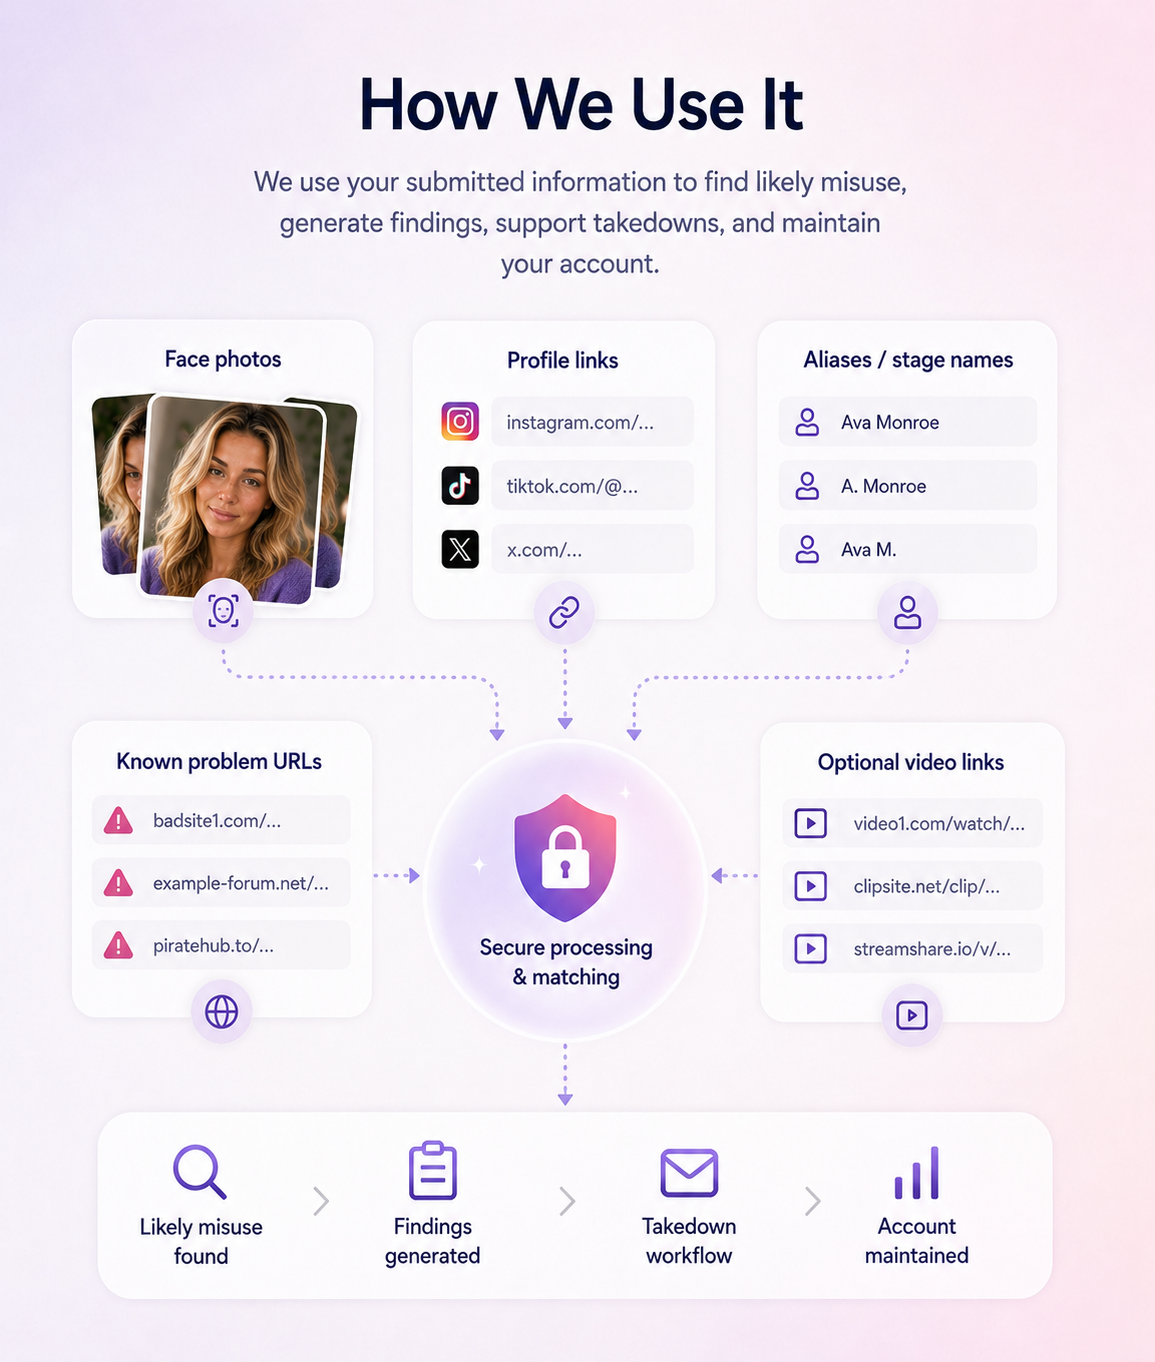
How we use it
The internal product path uses submitted references for supported scan, finding, review, report, Support, and account operations.
Current demos and scenarios are synthetic. No claim is made that every source, image, video, profile, or new upload is searched.
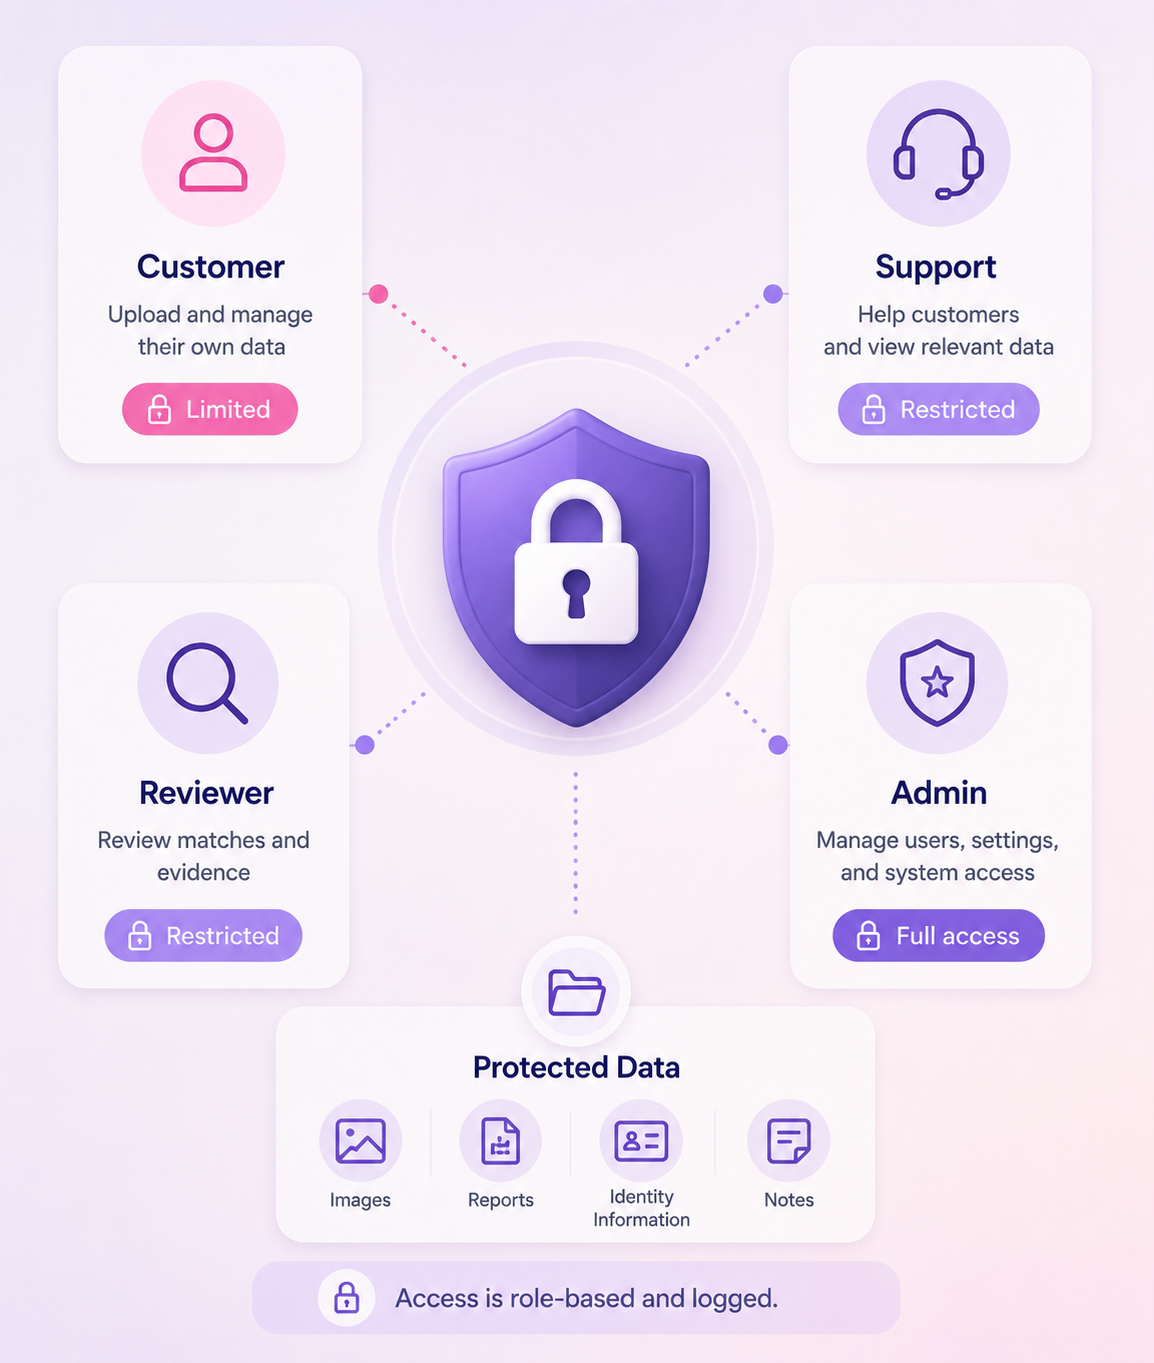
Access controls
Firebase Storage and Firestore rules deny direct browser reads and writes. Authenticated Functions derive customer context and broker supported portal operations.
Storage rules deny direct browser reads and writes across object paths.
Portal route checks require account context and applicable entitlements.
Upload preparation derives the customer path from authenticated context rather than browser-supplied identity.
The claim registry points to the security-gate and route tests that exercise these boundaries.
Claims deliberately not made
The current evidence does not establish an external audit, formal compliance program, public service level, universal encryption representation, or procurement document set.
Repository tests are engineering evidence, not an independent assessment.
No availability percentage or response-time commitment is offered.
Coverage depends on configured sources, eligible jobs, available media, and human review.
A finding, report, or prepared request does not prove delivery, platform action, or removal.
Customer control
Authenticated users can use portal data controls to request export or removal processing and can manage supported reference and profile data.
Removal is a reviewed process, not an instant purge promise. Retention varies by data class, workflow state, safety needs, and legal obligations as described in the Beta Privacy Policy.
Use the internal security contact route for a recorded inquiry and read its limitations before submitting.